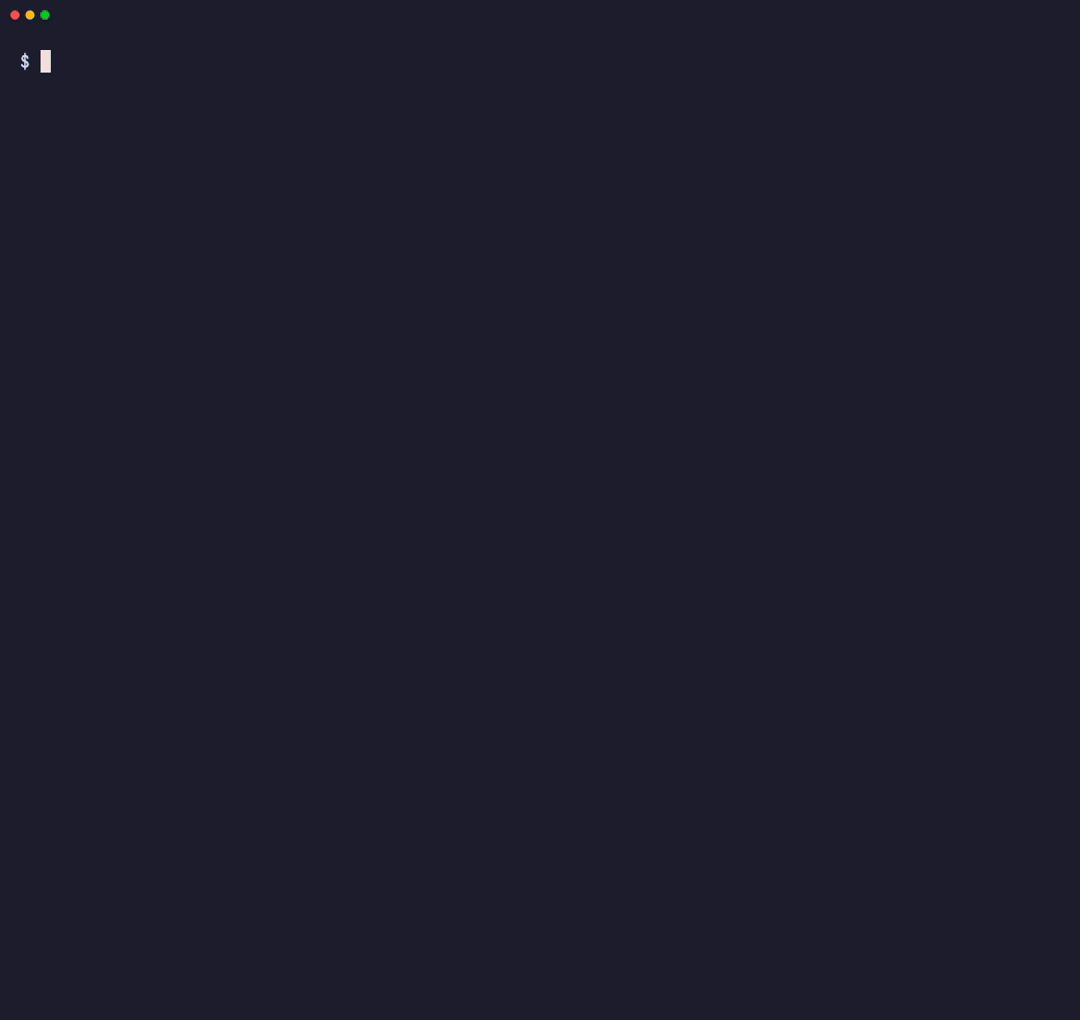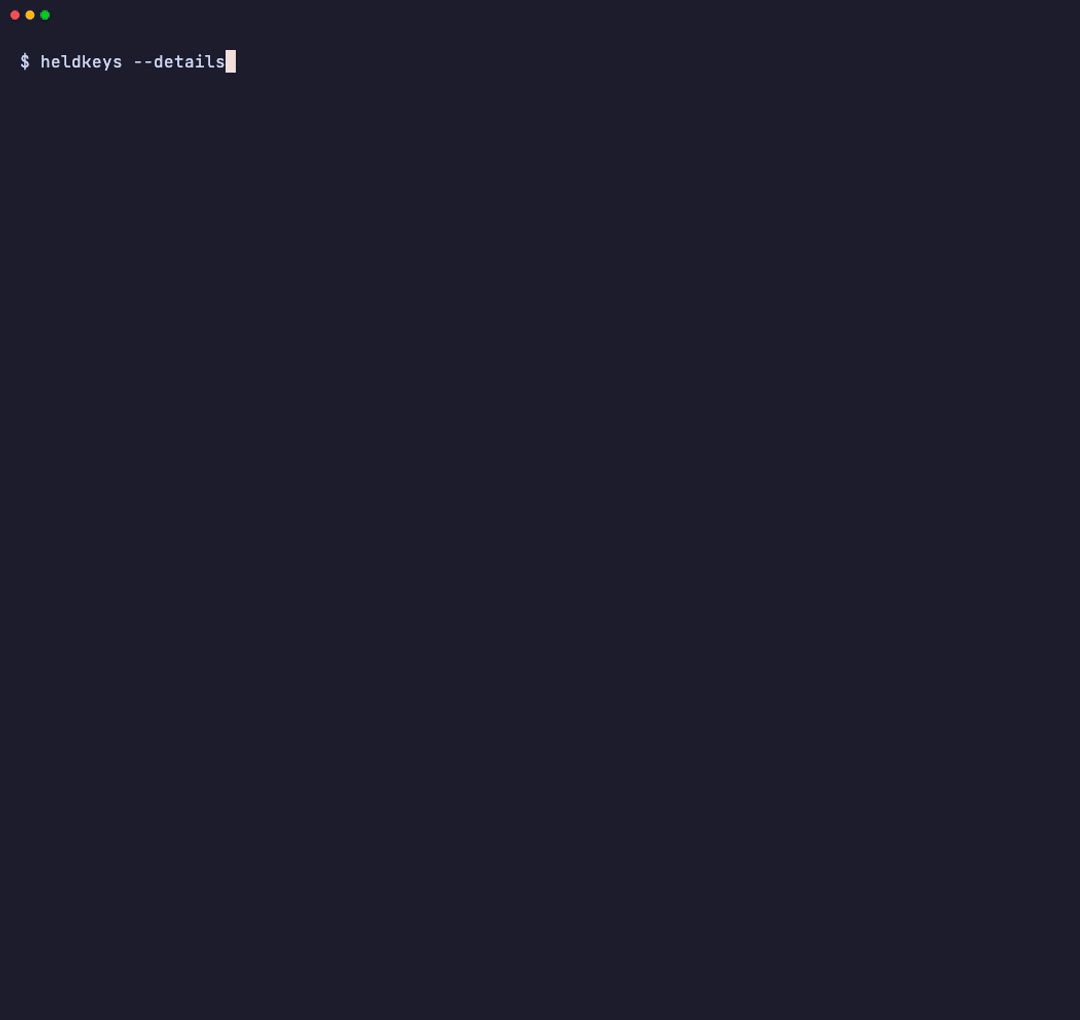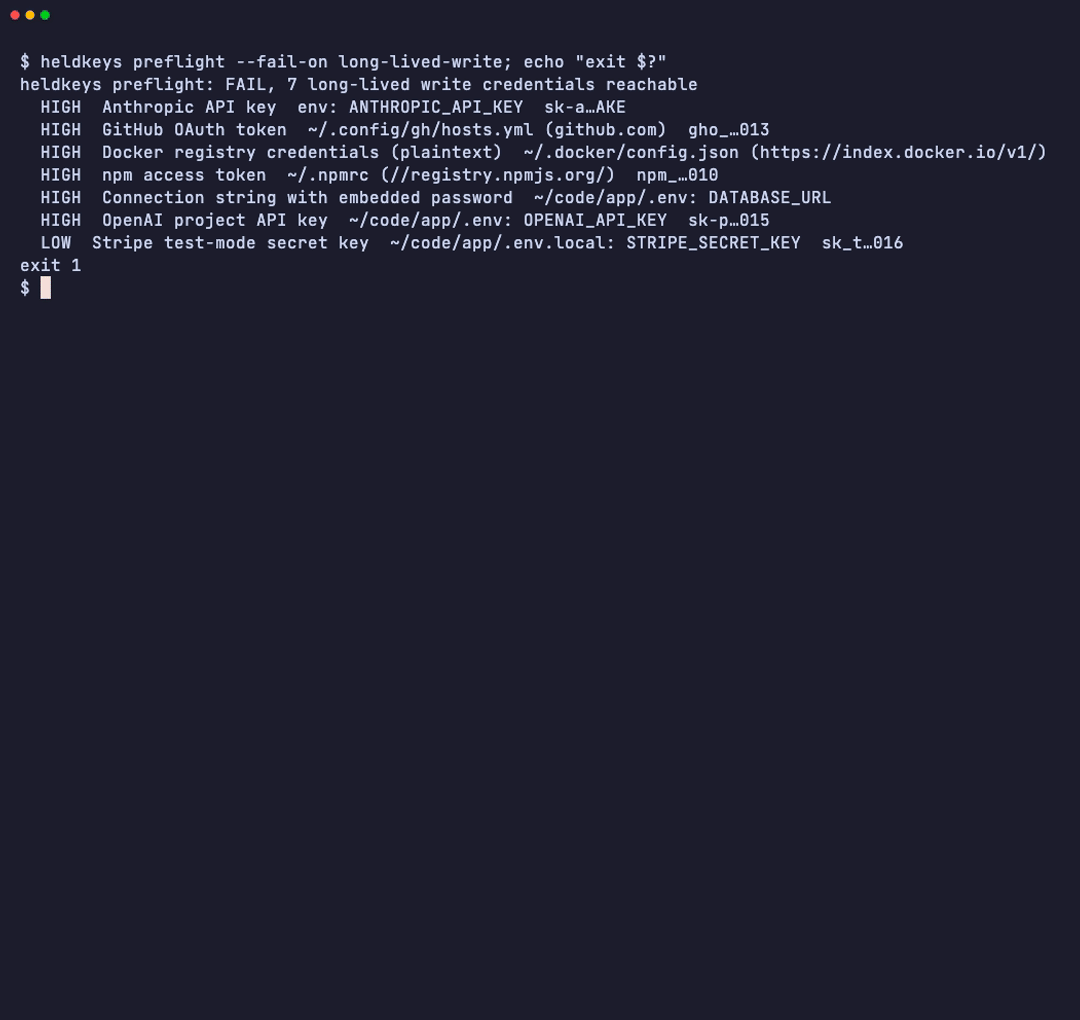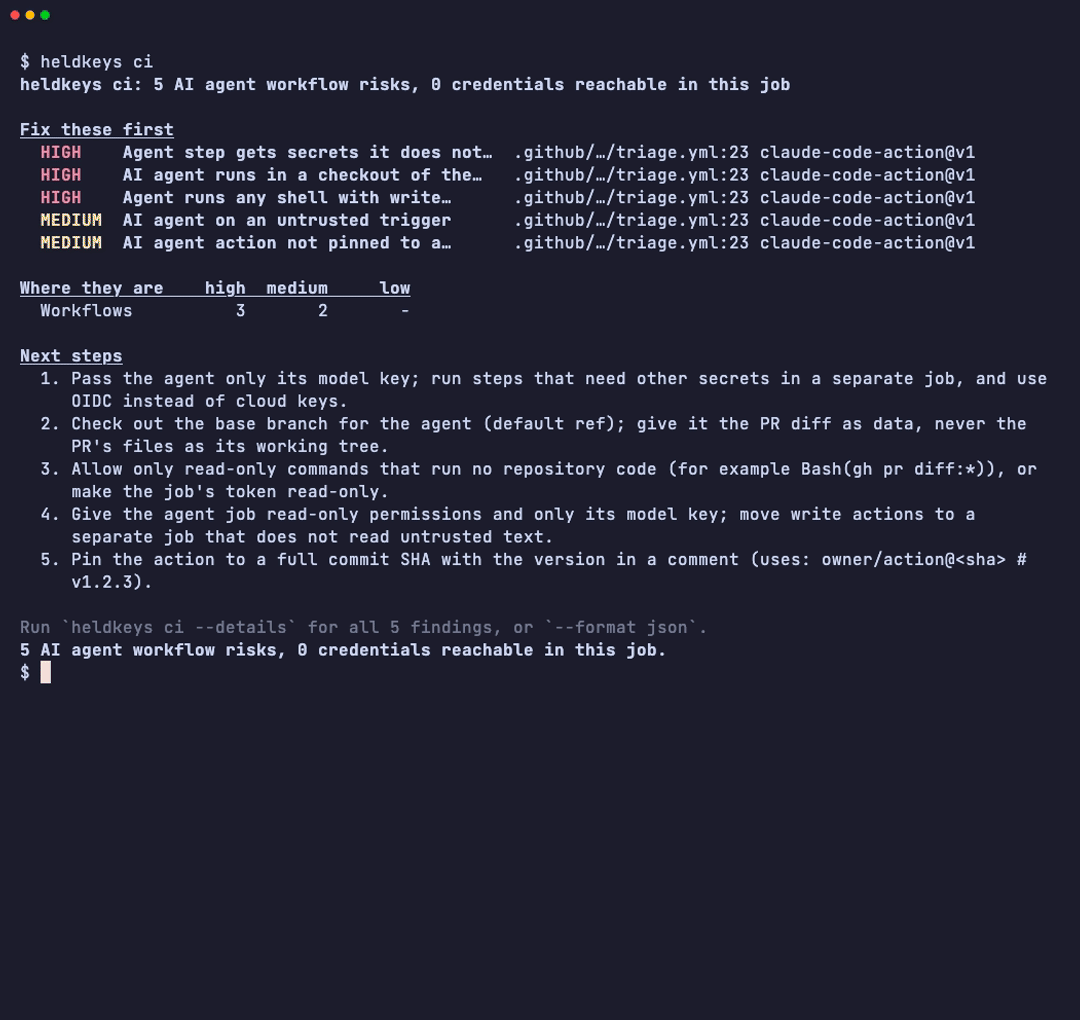
heldkeys is a self-contained, read-only command-line tool for Linux and macOS that shows which credentials an AI agent can reach from a terminal, project, sandbox, container, or CI job. It checks environment variables, cloud and developer CLI logins, AI tool credentials, package and Git tokens, .env files and editor-history copies, SSH keys, MCP server configurations, Docker and Kubernetes access, cloud metadata reachability, and CI-issued tokens. It never prints secret values: recognized tokens are shown only as limited fingerprints, while unknown-shaped passwords and tokens receive no fingerprint. The tool does not use telemetry, update checks, crash reports, or a daemon, and it creates files only when explicitly asked to write a report or baseline. Its CI mode inventories runtime credentials and analyzes GitHub workflow files for AI-agent risks, including externally triggerable agent steps with secrets or write access, pull-request checkouts, broad permissions, unnecessary secret inheritance, unpinned actions, and unrestricted shell execution. It follows local reusable workflows and can emit text, JSON, Markdown, or SARIF reports, with configurable failure thresholds, baselines, and reviewed-risk suppressions. The project also supports preflight checks for sandboxes and scanning running Docker containers or Kubernetes pods. heldkeys is designed to complement repository secret scanners and broader workflow tools: it focuses on what an agent can use at runtime and on risks specific to AI-agent steps. It supports Linux and macOS, not Windows, and cannot see every browser session, OS keychain, password manager, or capability that would require asking a credential issuer.